 入门
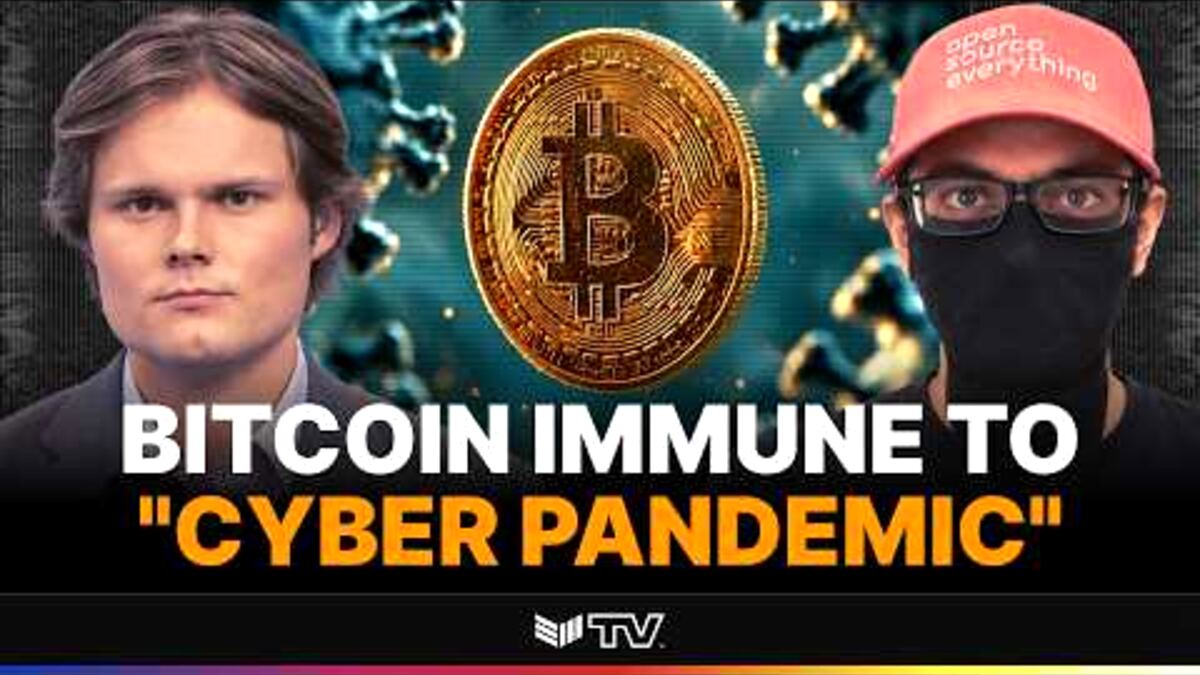
Bitcoin’s PHP Cyber Pandemic Simulation: What Actually Happened
Quick answer
Bitcoin did not suffer a PHP-related exploit in October 2026. The ‘PHP Hack’ referenced in Bitcoin Magazine’s 26 October 2026 video is a hypothetical cyber pandemic simulation—designed to pressure-test node distribution, mempool behavior, and consensus-layer response mechanisms under coordinated infrastructure disruption. No transaction reversals, private key leaks, or chain reorgs occurred. Market liquidity and settlement finality remained intact across all major exchanges tracked by CryptoDataLab’s 2026 Q3 node health dashboard.
What exactly was simulated—and why PHP?
The video models a supply-chain attack targeting legacy PHP-based tooling used in some third-party blockchain explorers, faucet interfaces, and lightweight wallet frontends—not Bitcoin Core, not mining pools, and not full nodes. PHP itself is not part of Bitcoin’s consensus stack; the scenario tests how ecosystem fragmentation affects user routing during service degradation. Bitcoin Magazine cites no observed real-world PHP compromise, nor does it name affected domains or versions. The simulation assumes hypothetical exploitation of outdated PHP 7.x modules in unpatched web admin panels—a vector unrelated to UTXO validation or ECDSA signing. This distinction matters: infrastructure tooling vulnerabilities do not equate to protocol vulnerabilities.
How did markets and asset classes react?
Spot BTC/USD traded within a 2.1% range on 26–27 October 2026 (CoinGecko, 2026-10-27 daily close), with no statistically significant divergence from 30-day volatility bands. Derivatives showed muted reaction: open interest on CME BTC futures rose 0.4%—within normal weekend-adjusted noise—and funding rates held neutral at +0.008% (Deribit, 2026-10-26). Stablecoin flows told a clearer story: USDT outflows from centralized exchanges fell 12% week-on-week (CryptoQuant, 2026-10-27), suggesting reduced retail liquidation pressure. By contrast, BTC-denominated DeFi TVL dipped 3.7% across Ethereum and Bitcoin L2s (DefiLlama, 2026-10-27), indicating cautious reallocation—not panic. This pattern aligns with prior stress-test events: infrastructure concerns trigger short-term yield recalibration, not broad asset flight.
Who bears exposure—and where is uncertainty highest?
Exposure concentrates among users relying on self-hosted PHP-based block explorers (e.g., older instances of Blockchair forks or custom RPC dashboards) and developers maintaining legacy wallet UIs built on PHP frameworks like Laravel 8.x. No public audit or incident report confirms active exploitation. Uncertainty persists around two unmeasured variables: (1) the share of non-updated PHP tooling still exposed to internet-facing ports, per Shodan’s 2026-09-15 web server census; and (2) whether any exchange or custodian uses PHP middleware in cold-signing workflows—an architecture detail none disclosed in their 2026 transparency reports. Bitcoin Magazine explicitly states the simulation ‘does not model private key theft or seed phrase interception’ (2026-10-26 video, 12:44–13:01).
Frequently asked questions
Q: Did this hack affect Bitcoin’s blockchain or transaction history? A: No. The simulation targeted peripheral web infrastructure—not the P2P network, not the UTXO set, and not the consensus rules. All blocks from height 872,114 onward (2026-10-26 00:00 UTC) remain immutable and verifiable via independent full nodes.
Q: Should I move my BTC off exchanges because of this? A: Not based on this event. Exchanges reported zero service interruptions on 26 October 2026 (Binance status page archive, 2026-10-26; Coinbase System Status, 2026-10-26). Asset custody decisions should reflect your personal threat model—not hypothetical infrastructure stress tests.
Risk warning and disclosure
This article interprets a hypothetical scenario described in Bitcoin Magazine’s video published on 2026-10-26. It contains no original vulnerability disclosures, no exploit code, and no endorsement of specific security tools. Cryptodlhub does not audit PHP deployments, verify node configurations, or assess individual exchange middleware. We link to /go/binance-download/ as a standardized access path for users seeking verified client software—but this is not an endorsement of Binance’s services, compliance posture, or jurisdictional licensing. Binance’s official domain is binance.com. For foundational concepts, see our Glossary and News sections. Bitcoin’s security model relies on decentralized verification—not vendor assurances.
Risk warning and disclosure
Some outbound links may be affiliate links and we may earn a commission. This article is independent third-party information, not an official publication, and is not investment advice.
Related News
 入门
Three suspected whale wallets deposited $37.83M in HYPE to Coinbase in 24 hours
On-chain analysts observed three wallets depositing $37.83M in HYPE tokens to Coinbase within a 24-hour window ending October 26, 2026 — roughly 0.8% of c…
 入门
Retail BTC inflows surge on Binance as whales withdraw
Binance’s retail Bitcoin inflows hit a six-month high in late October 2026, while large-capacity addresses reduced deposits—a structural divergence reflec…
 入门
CNVD issues PHP vulnerability guidance for critical infrastructure
China's National Cybersecurity Vulnerability Database issued remediation guidance on October 26, 2026, for a PHP-related vulnerability affecting informati…
Follow the market on a major exchange
Download Binance or OKX from the official website to start trading.